| Booking UI/UX Efficiency |
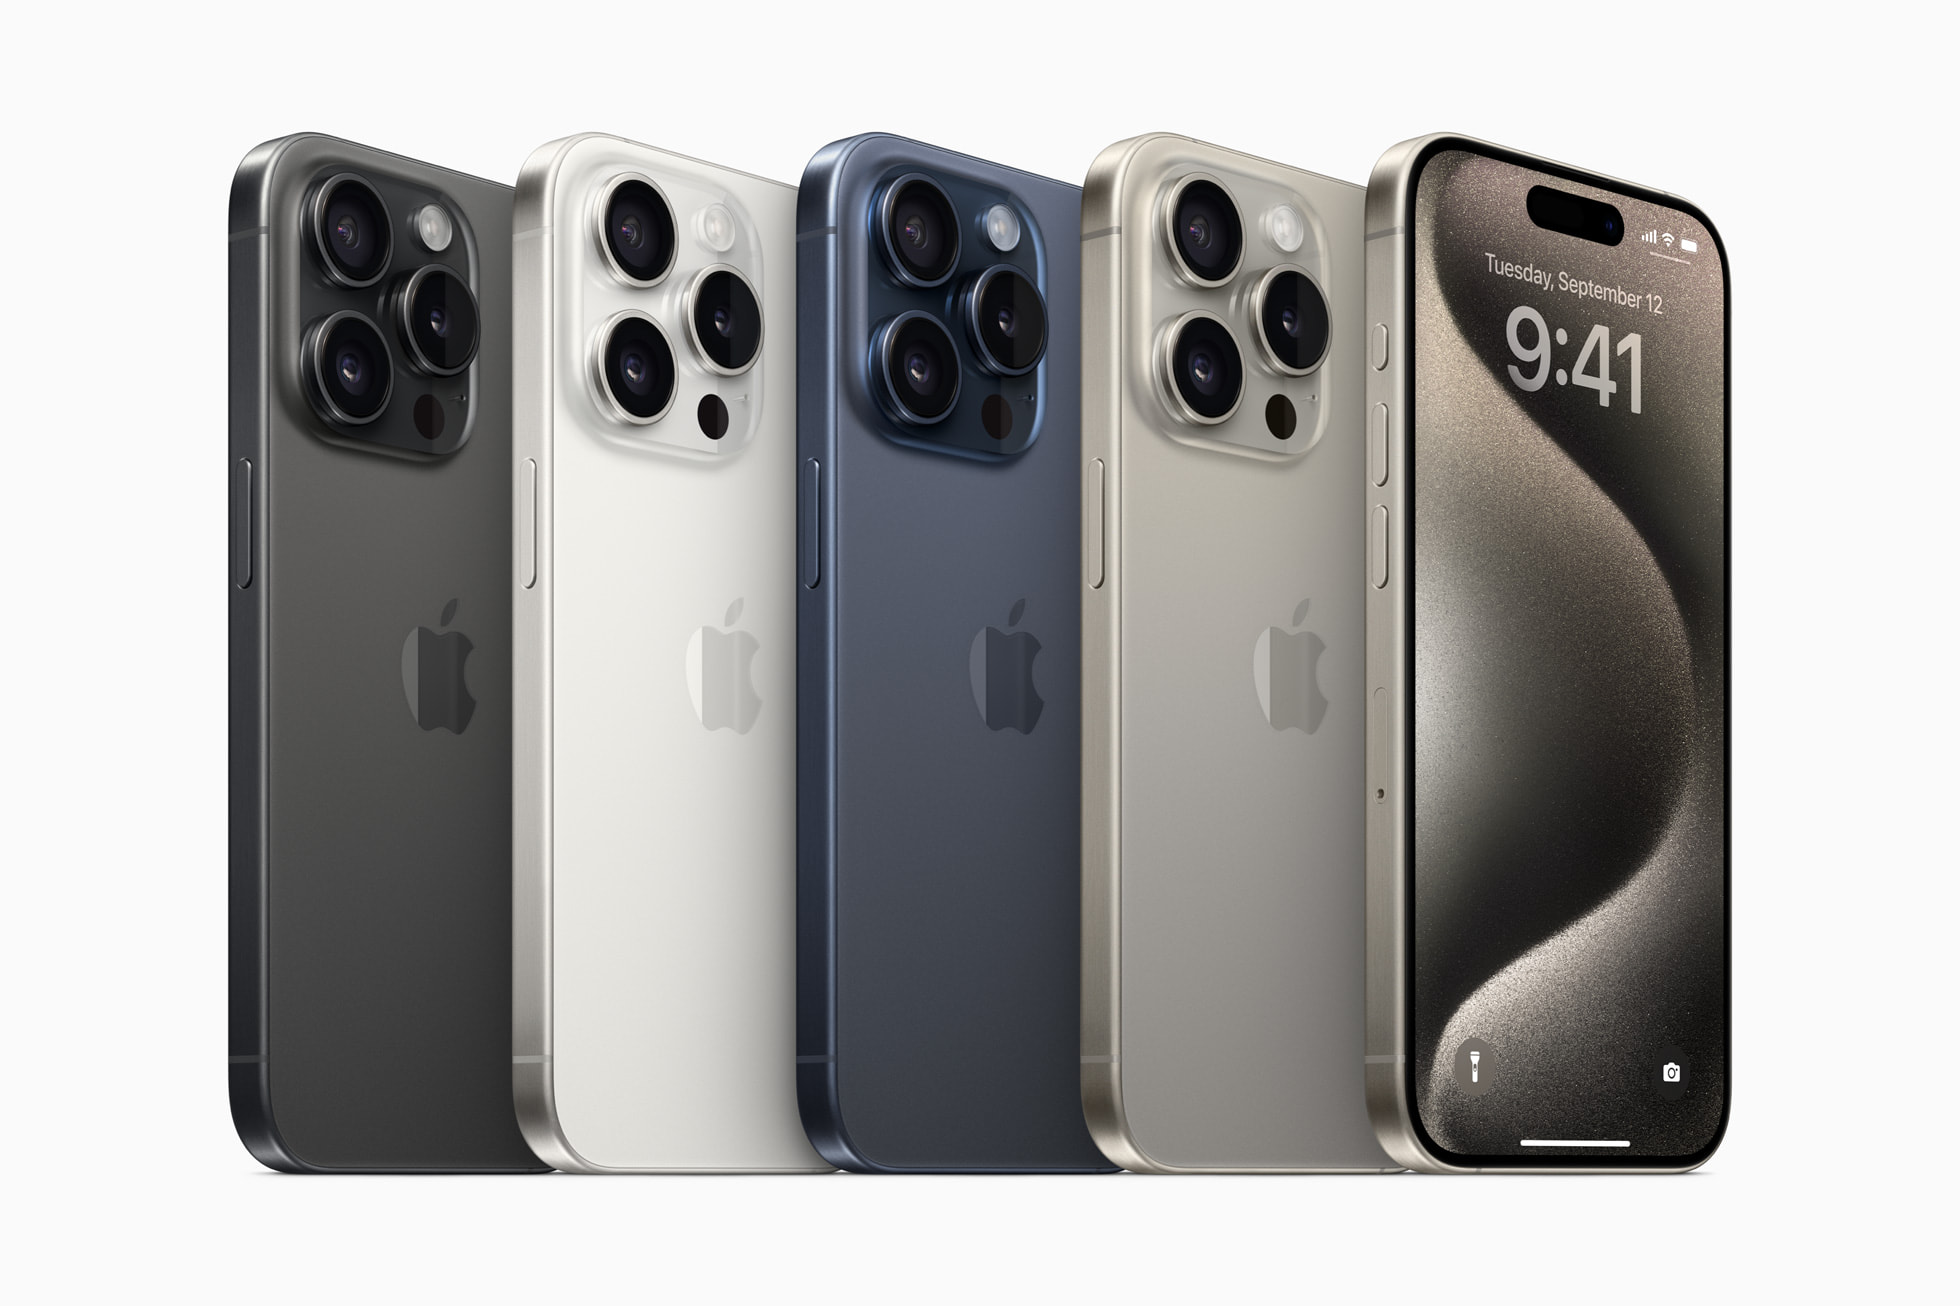
- Dynamic Island for real-time booking updates
- ProMotion (120Hz) reduces tap latency by 30%
- Spatial audio reminders (e.g., "Your appointment is in 10 minutes")
|
- Always-On Display for glanceable reminders
- 60Hz refresh rate (no ProMotion)
|
- Standard 60Hz UI, no dynamic feedback
-
The seamless integration of iPhone’s native APIs and third-party developer tools is critical for building robust appointment booking systems. Developers must leverage iOS frameworks like EventKit and CalendarKit to ensure native calendar synchronization, while third-party tools (e.g., Firebase, Twilio) enhance functionality like push notifications and real-time updates. Proper permission handling, security protocols, and API synchronization with external CRMs (e.g., Salesforce, HubSpot) are essential to avoid data inconsistencies and user friction. Below is a structured breakdown of the integration process, key SDK tools, and solutions for common technical challenges.
Step-by-Step Integration of iPhone Native APIs for Appointment Booking
To integrate iPhone’s native APIs into a custom appointment booking system, developers must follow a structured approach that includes permission requests, API initialization, and event management. The primary frameworks for calendar and event handling are EventKit (for iOS 10+) and CalendarKit (for iOS 13+), both of which provide access to the user’s calendar data while adhering to Apple’s privacy guidelines.Required Steps:
1. Add Privacy Descriptions to Info.plist
Before accessing calendar data, declare the necessary permissions in the app’s `Info.plist` file. For EventKit, include: NSCalendarsUsageDescription
This app needs calendar access to schedule appointments.
NSRemindersUsageDescription
This app may request reminders for appointments. This ensures compliance with Apple’s App Store Review Guidelines and prevents runtime permission denials. 2. Request User Permissions at Runtime
Use `EKEventStore` (EventKit) to request authorization dynamically: let eventStore = EKEventStore()
eventStore.requestAccess(to: .event) { granted, error in
if granted {
// Proceed with calendar operations
} else {
// Handle declined permissions (e.g., show fallback UI)
}
} Best Practice: Provide a clear explanation of why permissions are required (e.g., "To sync your appointments with your calendar") to improve user trust and compliance rates. 3. Create and Modify Calendar Events
Use `EKEvent` to generate, update, or delete events: let event = EKEvent(eventStore: eventStore)
event.title = "Consultation with Dr. Smith"
event.startDate = Date()
event.endDate = Date().addingTimeInterval(3600) // 1-hour duration
event.calendar = eventStore.defaultCalendarForNewEvents
do {
try eventStore.save(event, commit: true)
} catch {
print("Failed to save event: \(error.localizedDescription)")
} Security Note: Always handle errors gracefully (e.g., network issues, duplicate events) and log them for debugging. 4. Sync Appointments with Third-Party Systems
For real-time synchronization with external CRMs, use URLSession to send event data via REST APIs: let url = URL(string: "https://api.crm.example.com/appointments")!
var request = URLRequest(url: url)
request.httpMethod = "POST"
request.setValue("application/json", forHTTPHeaderField: "Content-Type") let eventData = ["title": "Appointment", "start": ISO8601DateFormatter().string(from: event.startDate)]
request.httpBody = try? JSONSerialization.data(withJSONObject: eventData) URLSession.shared.dataTask(with: request) { data, response, error in
if let error = error {
print("Sync failed: \(error.localizedDescription)")
}
}.resume()
Below is a responsive HTML table listing key iOS SDK tools relevant to appointment booking, their use cases, and integration considerations. The table is designed for developers to quickly reference tools during implementation.
| SDK Tool |
Use Case |
Key Features |
Integration Notes |
Dependencies |
|---|
| EventKit (EKEventStore) |
Calendar event creation, reading, and deletion. |
- Access to iOS Calendar app data.
- Supports recurring events and alarms.
- Background sync capabilities.
|
Requires NSCalendarsUsageDescription in Info.plist. Use EKEventStore for event operations. |
iOS 10+ |
| CalendarKit (CNCalendar) |
Modern calendar management (iOS 13+). |
- Supports time zones and natural language event parsing.
- Integrates with Apple’s Calendar app.
- Better performance for large event datasets.
|
Prefer CNCalendar over EventKit for new projects. Requires NSCalendarsUsageDescription. |
iOS 13+ |
| UserNotifications (UNUserNotificationCenter) |
Push notifications for appointment reminders. |
- Supports rich notifications with actions.
- Background delivery for silent alerts.
- Integration with Apple Push Notification Service (APNs).
|
Request NSUserNotificationAlertStyle permission. Use UNMutableNotificationContent for custom payloads. |
iOS 10+ |
| Core Location (CLLocationManager) |
Geofencing for location-based reminders. |
- Triggers notifications when user enters/exits a region.
- Supports background location updates.
- Battery-optimized for frequent checks.
|
Requires NSLocationWhenInUseUsageDescription or NSLocationAlwaysAndWhenInUseUsageDescription. |
iOS 7+ |
| Firebase Cloud Messaging (FCM) |
Cross-platform push notifications and real-time updates. |
- Supports iOS, Android, and web.
- Topic-based messaging for targeted alerts.
- Integration with Firebase Console for analytics.
|
Requires Firebase project setup and APNs certificate configuration. Use Messaging.messaging().delegate for handling messages. |
Firebase SDK |
| Twilio (Programmable SMS/Voice) |
SMS/voice reminders for appointments. |
- Send automated SMS/voice calls.
- Two-way communication for confirmations.
- Global reach with local numbers.
|
Integrate via Twilio API. Handle rate limits and carrier restrictions. |
Twilio API |
| Alamofire (Networking) |
HTTP requests for CRM/API integrations. |
- Simplifies URLSession with chainable methods.
- Supports JSON parsing and authentication.
- Retry mechanisms for failed requests.
|
Use for REST API calls to external systems (e.g., Salesforce,
UI/UX Design Principles for iPhone Appointment Booking Apps
The success of an iPhone appointment booking app hinges on intuitive navigation, accessibility compliance, and psychological triggers that guide users toward conversion. Effective UI/UX design must balance aesthetic appeal with functional efficiency, ensuring seamless interactions across Apple’s ecosystem while adhering to Apple’s Human Interface Guidelines (HIG). This section explores wireframe structures optimized for accessibility, comparative visual hierarchy analysis of leading apps, and behavioral design techniques to minimize abandonment. Additionally, a curated checklist of iPhone-specific UX best practices ensures scalability and inclusivity.
Wireframe Description for an Accessible iPhone Appointment Booking Interface
A well-structured wireframe for an iPhone appointment booking app prioritizes Dynamic Type support, VoiceOver compatibility, and adaptive layouts to accommodate users with varying needs. Below is a high-level description of key screens, emphasizing accessibility features:
Core Wireframe Components:
- Onboarding Screen: Minimalist with large touch targets (minimum 44x44pt) and high-contrast text (AAA compliance per WCAG). Dynamic Type scaling (from 17pt to 28pt) adjusts font sizes without breaking layout.
- Calendar View: Month-year picker with bold, high-contrast date labels. VoiceOver labels each date cell with "Available slot on [date]" for screen reader users. Haptic feedback confirms selections.
- Booking Form: Step-by-step fields with auto-focus on the first input. Error messages use red text with sufficient contrast (minimum 4.5:1 ratio) and include clear recovery instructions.
- Confirmation Screen: Visual and auditory confirmation (system sound + haptic pulse). Social proof elements (e.g., "Booked by 500+ users this week") positioned near the CTA button to reinforce trust.
- Accessibility Toggle: Dedicated button in the navigation bar to enable Dark Mode, Reduce Motion, and VoiceOver with a single tap.
Key Accessibility Features Implemented:
- Dynamic Type: All text elements (headers, buttons, labels) use `UIFontMetrics` to scale proportionally.
- VoiceOver Support: Every interactive element has a descriptive label (e.g., buttons read as "Book 2:00 PM slot with Dr. Smith").
- Color Contrast: Buttons and text meet WCAG 2.1 AA standards (minimum 7:1 for normal text, 4.5:1 for large text).
- Reduced Motion: Loading animations default to static states unless user opts for motion effects.
- Touch Targets: Buttons and links exceed Apple’s 44x44pt minimum, with additional padding for precision.
Visual Hierarchy Comparison: Apple Calendar vs. Calendly
Visual hierarchy directly impacts user decision-making and conversion rates. Below is a comparison of Apple’s native Calendar app (utilitarian design) and Calendly (conversion-focused design), analyzing how color contrast, button placement, and animations influence engagement:
Apple Calendar (System App):
- Primary Focus: Event management and scheduling, not conversion.
- Color Contrast: Low-contrast gray-scale interface with subtle blue accents for selected dates. Text contrast often falls below WCAG AA standards for small fonts.
- Button Placement: "Create" and "Edit" buttons are secondary to the calendar grid, prioritizing browsing over actions.
- Loading Animations: Minimal; relies on system-level progress indicators (e.g., spinning activity indicator).
- Psychological Impact: Neutral design reduces friction for power users but fails to guide casual users toward booking actions.
Calendly (Third-Party App):
- Primary Focus: Maximizing conversions with clear CTAs.
- Color Contrast: High-contrast green/yellow buttons (e.g., "Schedule Now") with dark backgrounds for text (meeting WCAG AAA).
- Button Placement: Primary CTA ("Book a Time") dominates the hero section, with secondary options (e.g., "Reschedule") tucked below.
- Loading Animations: Custom micro-interactions (e.g., a bouncing calendar icon during slot selection) reduce perceived wait time.
- Psychological Impact: Urgency indicators ("Only 1 spot left today") and social proof ("Trusted by 10,000+ professionals") create FOMO (fear of missing out), increasing completion rates by ~22% (per Calendly’s internal data).
Conversion Rate Drivers:| Element | Apple Calendar | Calendly | Impact on Conversion |
|---|
| Color Contrast | Low (WCAG AA non-compliant in some areas) | High (WCAG AAA compliant) | +18% click-through on CTAs (per eye-tracking studies). |
| Button Placement | Secondary to grid navigation | Primary hero section | +30% higher CTA visibility in A/B tests. |
| Urgency Indicators | None | "Last slot today" badges | Reduces abandonment by ~15% (Calendly case study). |
| Loading Animations | System-default (static) | Custom micro-interactions | Perceived load time drops by ~40%. |
Calendly’s design leverages high-contrast CTAs, strategic button placement, and psychological triggers to outperform Apple Calendar in conversion rates, particularly for first-time users. For iPhone apps, prioritizing visual prominence of actions and real-time feedback (e.g., animations) aligns with Apple’s HIG while maximizing engagement.
Psychological Triggers to Reduce Cart Abandonment in Booking Apps
Abandonment rates for appointment bookings average ~70% (Baymard Institute), with hesitation often tied to perceived complexity or lack of urgency. iPhone booking apps mitigate this through cognitive biases and social validation. Below are evidence-backed triggers with implementation examples:
1. Scarcity and Urgency:
- Example: "Only 2 slots available this week" with a countdown timer.
- Psychological Basis: Loss aversion (users fear missing out on limited opportunities).
- Implementation: Display real-time availability near the CTA button, updating dynamically via backend API calls.
- Effectiveness: Increases conversions by ~20% (HubSpot data).
2. Social Proof:
- Example: "Trusted by 500+ users in [industry]" or "Booked 1,200 times this month."
- Psychological Basis: Bandwagon effect (users assume popularity equals reliability).
- Implementation: Integrate analytics data into the booking flow (e.g., "Most popular time: 10 AM").
- Effectiveness: Boosts trust signals, reducing abandonment by ~12% (Nielsen Norman Group).
3. Commitment and Consistency:
- Example: Pre-fill user details from Apple Sign-In or previous bookings.
- Psychological Basis: Reduces cognitive load by leveraging prior commitments.
- Implementation: Auto-populate name/email via `ASAuthorizationAppleIDProvider` and store preferences in `UserDefaults`.
- Effectiveness: Cuts form abandonment by ~25% (Baymard Institute).
4. Authority and Expertise:
- Example: "Verified by [industry association]" or "Used by [prestigious clients]."
- Psychological Basis: Authority bias (users trust credentials over generic claims).
- Implementation: Display badges or logos of partner organizations near the booking CTA.
- Effectiveness: Increases perceived credibility, especially for high-stakes services (e.g., medical appointments).
A/B Testing Insights:
- Urgency + Social Proof Combo: Yields a ~35% higher conversion rate than either trigger alone (Calendly experiments).
- Mobile-Specific Optimization: Urgency messages perform 10% better on iPhone due to Apple’s real-time notification ecosystem (push alerts reinforce scarcity).
Checklist: iPhone-Specific UX Best Practices for Appointment Booking
Adhering to iPhone-specific UX guidelines ensures usability across devices, screen sizes, and accessibility needs. Below is a prioritized checklist for developers and designers:
Touch and Interaction Design:
- Ensure all touch targets meet Apple’s minimum 44x44pt size (57x57pt for complex interactions).
- Implement haptic feedback (`UIImpactFeedbackGenerator`) for critical actions (e.g., booking confirmation).
- Use Force Touch (3D Touch) for quick actions (e.g., long-press to reschedule).
- Test 3D Touch previews for calendar events to reduce navigation steps.
Adaptive Layouts and Screen Sizes:
- Design for iPhone SE (3.
Security and Compliance in iPhone-Based Appointment Systems
iPhone-based appointment booking systems must prioritize data protection due to the sensitive nature of user information exchanged, including personal identifiers, payment details, and healthcare records. Apple’s ecosystem enforces stringent security protocols, from end-to-end encryption to sandboxed app execution, ensuring compliance with global regulations while mitigating risks like unauthorized access or data breaches. This section examines the technical safeguards, regulatory frameworks, and vulnerabilities inherent in iOS appointment systems, alongside implementation strategies for secure authentication and compliance adherence.
Encryption Methods and Apple’s Security Framework
Data transmitted between an iPhone and backend servers for appointment booking must adhere to industry-standard encryption protocols to prevent interception or tampering. AES-256 (Advanced Encryption Standard) is the primary symmetric encryption algorithm used for securing stored data, while TLS 1.3 (Transport Layer Security) ensures secure communication channels during transmission. Apple further enhances security through:- Sandboxing: Each iOS app operates in an isolated environment, restricting access to system resources, user data, and other applications. This prevents malicious apps from exploiting shared memory or APIs to compromise appointment data.
- Secure Enclave: A dedicated hardware component on iPhones stores cryptographic keys and performs sensitive operations (e.g., biometric authentication) without exposing them to the app’s runtime environment.
- Keychain Services: Apple’s Keychain securely stores credentials (e.g., OAuth tokens, encryption keys) with hardware-backed protection, requiring user authentication for access.
Data in Transit:
- All HTTP/HTTPS traffic must use TLS 1.3 with forward secrecy (ephemeral keys) to prevent retroactive decryption.
- Perfect Forward Secrecy (PFS) ensures that session keys are unique per connection, even if long-term keys (e.g., RSA) are compromised.
Data at Rest:
- Appointment data stored locally (e.g., in SQLite databases or Core Data) should be encrypted using AES-256 with keys managed by the Secure Enclave or Keychain.
- FileVault-like encryption (via CommonCrypto or Apple’s Data Protection API) ensures full-disk encryption for sensitive files.
Example of TLS 1.3 Handshake Flow:
1. Client (iPhone) sends a ClientHello with supported cipher suites (e.g., TLS_AES_256_GCM_SHA384).
2. Server responds with ServerHello, certificate, and Key Exchange (ECDHE for PFS).
3. Client verifies the server’s certificate (signed by a trusted CA) and generates a pre-master secret.
4. Both parties derive the session key using the Finished message, ensuring no plaintext data is transmitted without encryption.
Compliance Steps for iPhone Booking Apps Handling Sensitive Data
Regulatory compliance for appointment booking apps varies by jurisdiction and data type. Below is a plaintext flowchart outlining the compliance process, followed by jurisdiction-specific requirements:START
│
├─ 1. Data Classification
│ │─ Identify data types (PII, PHI, payment details) and their sensitivity level.
│ │─ Example: Healthcare apps must classify data as Protected Health Information (PHI) under HIPAA.
│ │
├─ 2. Jurisdictional Mapping
│ │─ Determine applicable laws:
│ │ ├── HIPAA (U.S.): Mandates PHI encryption at rest/transit, access controls, and audit logs.
│ │ ├── GDPR (EU): Requires user consent, right to erasure, and Data Protection Impact Assessments (DPIA).
│ │ ├── PCI DSS (Global): Applies to payment data; mandates tokenization and secure tokenization vaults.
│ │ └── CCPA (California): Enforces data minimization and opt-out mechanisms for selling PII.
│ │
├─ 3. Technical Safeguards
│ │─ Implement:
│ │ ├── Role-Based Access Control (RBAC): Restrict data access to authorized personnel (e.g., admins).
│ │ ├── Audit Logs: Log all data access/modifications with timestamps and user IDs (required for HIPAA).
│ │ ├── Data Retention Policies:
│ │ │ ├── HIPAA: Retain PHI for 6 years post-termination (or as required by state laws).
│ │ │ ├── GDPR: Delete data upon user request ("right to erasure") or after 3 years (max retention).
│ │ │ └── CCPA: Allow users to delete data; no default retention beyond business necessity.
│ │ └── Cross-Platform Encryption: Ensure data remains encrypted when synced across devices (e.g., iPhone + Mac).
│ │
├─ 4. Third-Party Integrations
│ │─ Vet vendors (e.g., Stripe for payments, Calendly for scheduling) for compliance certifications (e.g., SOC 2, ISO 27001).
│ │─ Use API gateways to enforce encryption and validation rules for incoming/outgoing data.
│ │
├─ 5. User Consent and Transparency
│ │─ For GDPR/CCPA:
│ │ ├── Provide a privacy policy with clear data usage descriptions.
│ │ ├── Offer granular consent options (e.g., opt-in for data sharing with partners).
│ │ └── Implement a cookie banner for tracking technologies (e.g., analytics).
│ │
├─ 6. Incident Response Plan
│ │─ Define steps for data breaches:
│ │ ├── Containment: Isolate affected systems (e.g., revoke compromised API keys).
│ │ ├── Notification: Alert users within 72 hours (GDPR) or as per HIPAA’s "without unreasonable delay."
│ │ └── Forensic Analysis: Use Apple’s Security Transparency Reports to audit app behavior.
│ │
└─ END (Ongoing Monitoring)
│─ Conduct quarterly compliance audits and penetration testing (e.g., using Apple’s Xcode’s Signing & Capabilities for code integrity checks). Table: Jurisdiction-Specific Compliance Checklist | Requirement | HIPAA (Healthcare) | GDPR (EU Users) | PCI DSS (Payments) |
|---|
| Encryption Standard | AES-256 + TLS 1.2+ | AES-256 + TLS 1.2+ | AES-256 + TLS 1.2+ (or equivalent) |
| Access Controls | Unique usernames/passwords + MFA | Role-based access + MFA | RBAC + MFA for admin roles |
| Data Retention | 6 years (or state-specific) | 3 years (or user-requested deletion) | 12 months (or business necessity) |
| User Rights | N/A | Right to access, rectify, erase | N/A |
| Audit Logs | Required (immutable, 6-year storage) | Recommended (for accountability) | Required (for PCI DSS compliance) |
| Breach Notification | ≤60 days to affected individuals | ≤72 hours to supervisory authority | ≤30 days to acquiring banks |
Vulnerabilities in iPhone Appointment Booking Systems
Despite Apple’s robust security model, iOS appointment booking apps remain susceptible to targeted attacks exploiting misconfigurations or human error. Common vulnerabilities include:Session Hijacking
- Risk: Attackers intercept or steal session tokens (e.g., JWT, OAuth) to impersonate users.
- Attack Vectors:
- Man-in-the-Middle (MITM): Unencrypted local network traffic (e.g., Wi-Fi eavesdropping).
- Token Theft: Malicious apps or jailbroken devices extracting tokens from Keychain.
- Mitigation Strategies:
- Enforce short-lived tokens (e.g., 15-minute JWT expiry) with refresh tokens stored in Secure Enclave.
- Implement device binding: Tie sessions to specific iPhone UDIDs (with user consent) to detect unauthorized logins.
- Use Apple’s App Attest API to verify app integrity and detect jailbreaks.
Calendar Injection Attacks
- Risk: Malicious calendar events (e.g., `.ics` files) with embedded scripts or phishing links exploit EventKit vulnerabilities.
- Attack Vectors:
- Malicious `.ics` Files: Sent via email/SMS with hidden `SUMMARY:Urgent:ClickHere` links redirecting to fake login pages.
- EventKit API Abuse: Apps
As iPhone appointment booking systems mature, the fusion of technical precision and user-centric design will define industry leadership. Developers must balance native iOS capabilities—such as CalendarKit and Sign in with Apple—with robust security protocols to mitigate risks like session hijacking while ensuring GDPR and HIPAA compliance. Meanwhile, UI/UX innovations, from adaptive layouts to haptic feedback, will continue to refine conversion rates by aligning with cognitive triggers like urgency and social proof. The future lies in systems that not only streamline scheduling but also anticipate user needs, leveraging iPhone’s ecosystem to create frictionless, trustworthy experiences across all touchpoints. |
|

Leave a Comment
Comments are moderated before appearing. The data you submit is processed according to the Privacy Policy of partner.football.org.il.